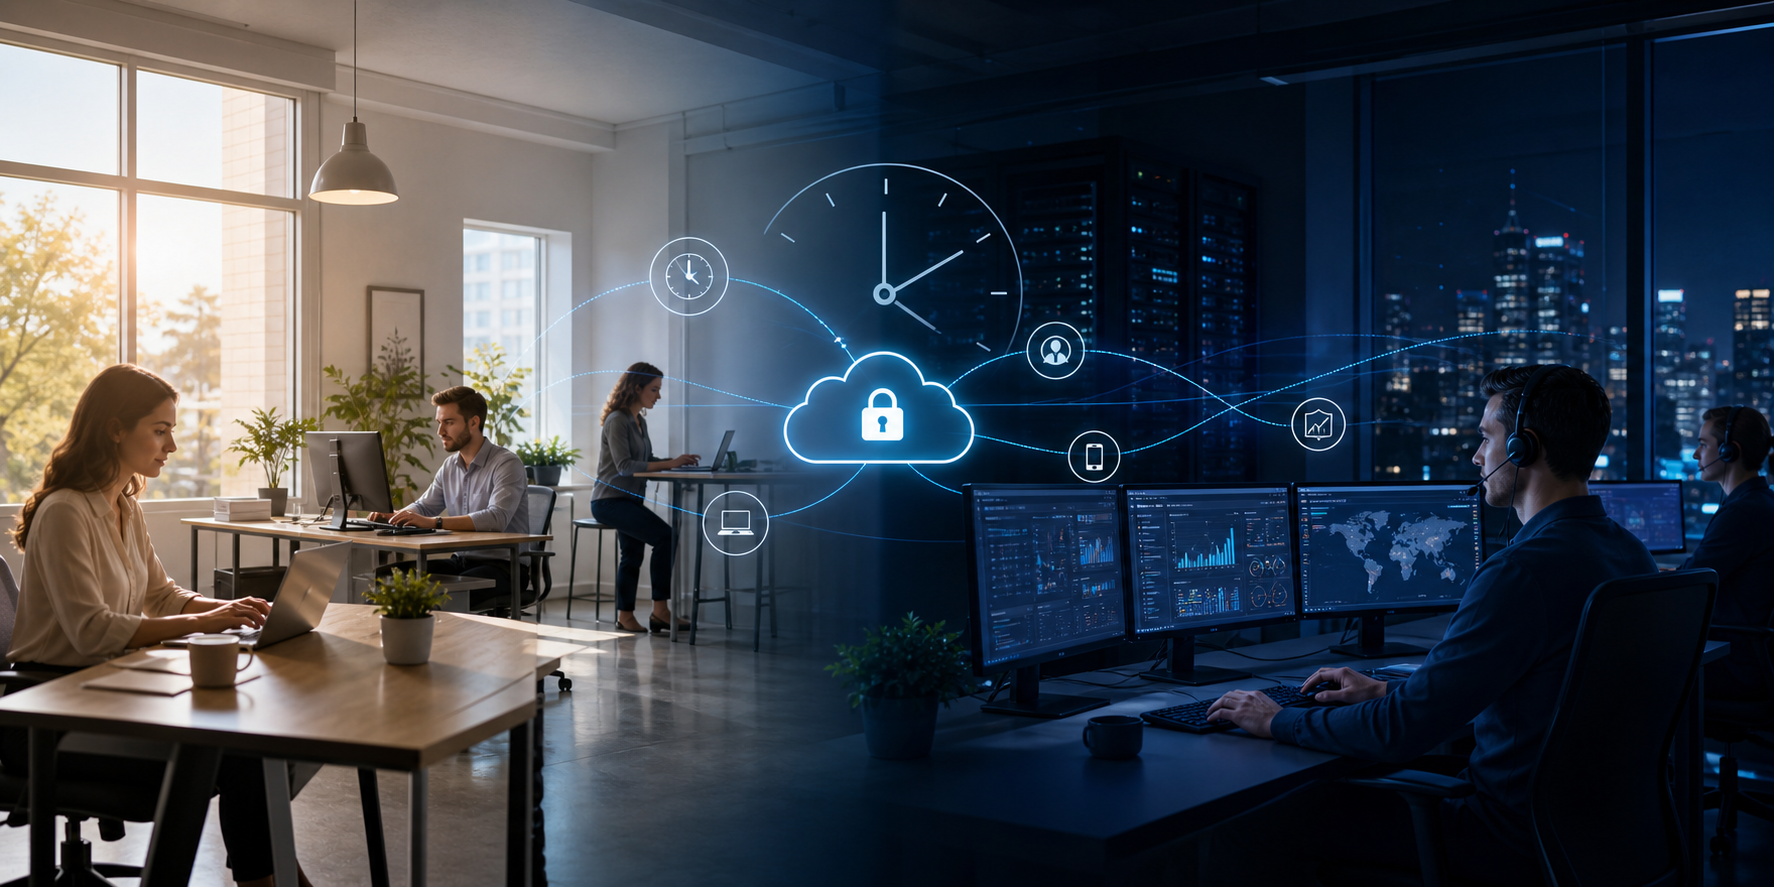
A server alert at 2:00 a.m. and a password reset at 2:00 a.m. are both “after-hours IT issues,” but they do not require the same response. That distinction is the key to understanding 24/7 outsourced IT support.
For most small and mid-sized businesses, always-on support should not mean paying a full team to answer every routine request instantly overnight. It should mean that critical systems are monitored, urgent incidents reach the right person, and employees know exactly where to turn outside normal business hours.
What Is 24/7 Outsourced IT Support?
24/7 outsourced IT support gives a business access to external monitoring, helpdesk, or incident-response resources around the clock. The provider may handle support directly, use an on-call rotation, or combine automated monitoring with human escalation.
The phrase can refer to three different service levels:
- 24/7 monitoring: tools watch servers, networks, backups, endpoints, or security systems continuously and create alerts when defined conditions occur.
- 24/7 emergency response: a technician responds to business-critical outages or security incidents at any hour.
- 24/7 user helpdesk: employees can contact a live support team for routine and urgent issues at any time.
These are not interchangeable. A plan that includes continuous monitoring may still route ordinary user tickets to the next business day.
What 24/7 Coverage Usually Includes
Continuous Monitoring and Automated Alerts
Monitoring tools can track whether servers, cloud resources, network devices, backup jobs, and critical services are available and healthy. They may also flag storage capacity, failed processes, unusual activity, or endpoint-security events.
The value comes from what happens after the alert. Ask whether alerts are only logged, reviewed by a human, or tied to an automatic remediation and escalation process.
Critical Incident Triage
When a major outage or suspected security event occurs, an after-hours responder confirms the problem, measures its impact, starts containment or recovery, and brings in the appropriate specialist. The first objective is to protect the business and restore essential operations—not to solve every low-priority symptom overnight.
On-Call Escalation
A documented escalation path identifies who is contacted for internet outages, inaccessible line-of-business systems, account compromise, facility issues, or vendor failures. Good escalation procedures also define which client decision-makers may approve emergency changes or costs.
Backup Failure and Recovery Alerts
Backups often run at night. Around-the-clock monitoring can identify failed jobs before the business discovers a missing restore point during an emergency. Depending on the plan, technicians may restart a failed job, investigate storage or connectivity problems, or begin recovery.
Security Alert Response
Attackers do not follow business hours. A 24/7 security component may include review of endpoint, identity, email, firewall, or cloud alerts; disabling a suspicious account; isolating a device; preserving evidence; and escalating a confirmed incident.
Standard IT monitoring is not automatically a security operations center. Confirm which sources are watched and whether the provider offers active response or notification only.
After-Hours User Assistance
Some plans provide live assistance for employees on evening, overnight, weekend, or holiday shifts. Others offer emergency support only. Routine requests such as software installation, device setup, and access changes may wait for daytime staff unless they block a critical operation.
What Counts as an After-Hours Emergency?
A useful agreement defines severity by business impact. Common critical examples include:
- A companywide internet or network outage
- A production server or essential cloud application being unavailable
- A suspected ransomware event or active account compromise
- Multiple employees unable to perform time-sensitive work
- A failed system affecting customers, revenue, patient care, or regulatory obligations
A single user requesting a new application, a printer problem, or a nonurgent access change would typically be handled during normal support hours. Clear priority rules protect response capacity for the incidents that truly cannot wait.
Who Benefits Most from 24/7 IT Support?
Always-on coverage is most valuable when downtime outside office hours still creates real business impact. That often includes:
- Healthcare organizations and other operations with evening or weekend shifts
- Professional services firms with remote or traveling employees
- Businesses serving customers across multiple time zones
- E-commerce, logistics, manufacturing, and other operations that rely on continuous systems
- Organizations with strict recovery, security, or availability requirements
- Small internal IT teams that need dependable nights-and-weekends backup
A local office that closes at 5:00 p.m. may not need a fully staffed overnight helpdesk. It may get more value from 24/7 monitoring plus emergency escalation.
Is 24/7 Outsourced IT Support Worth It for an SMB?
The answer depends on the cost of waiting. Estimate what one hour of downtime would mean in lost revenue, delayed work, customer impact, overtime, or compliance risk. Then compare that exposure with the added cost of the coverage level you actually need.
For many SMBs, the best-value model is layered:
- Continuous automated monitoring
- Human response for critical alerts
- On-call escalation for major outages and security events
- Business-hours handling for routine user tickets
Organizations with true overnight operations may justify a live 24/7 helpdesk. Others can avoid overbuying by defining a narrower emergency scope.
Questions to Ask a 24/7 IT Support Provider
- Does “24/7” mean monitoring, emergency response, or a live user helpdesk?
- Which systems and alert sources are monitored?
- What severity levels receive an immediate human response?
- What are the response targets for critical incidents?
- Who answers after hours: the regular team, an on-call specialist, or a third party?
- Are after-hours calls included, limited, or billed separately?
- How are client contacts notified and updated during an incident?
- Can the team make emergency changes, and who approves them?
- How are events documented and reviewed afterward?
- What happens if the primary technician or escalation contact is unavailable?
24/7 Support Should Match Your Real Risk
Always-on IT coverage is valuable when it creates a reliable path from alert to action. The goal is not to treat every request as an emergency. It is to detect serious problems early, protect critical operations, and give the business predictable support when the normal workday ends.
Microwize helps small and mid-sized businesses design practical remote support coverage without unnecessary complexity. Learn how our outsourced IT helpdesk services work, review the broader remote IT support services guide, or contact Microwize to discuss the right hours, escalation model, and support scope for your organization.